
Pull to refresh
Logo
Ransomware attack takes down Queens Public Library systems

Ransomware attack takes down Queens Public Library systems

Force in Play New York, NY local

All 66 branches stay open, but Wi-Fi, checkouts, the website and digital media are offline

Overview

Updated 1 hour ago

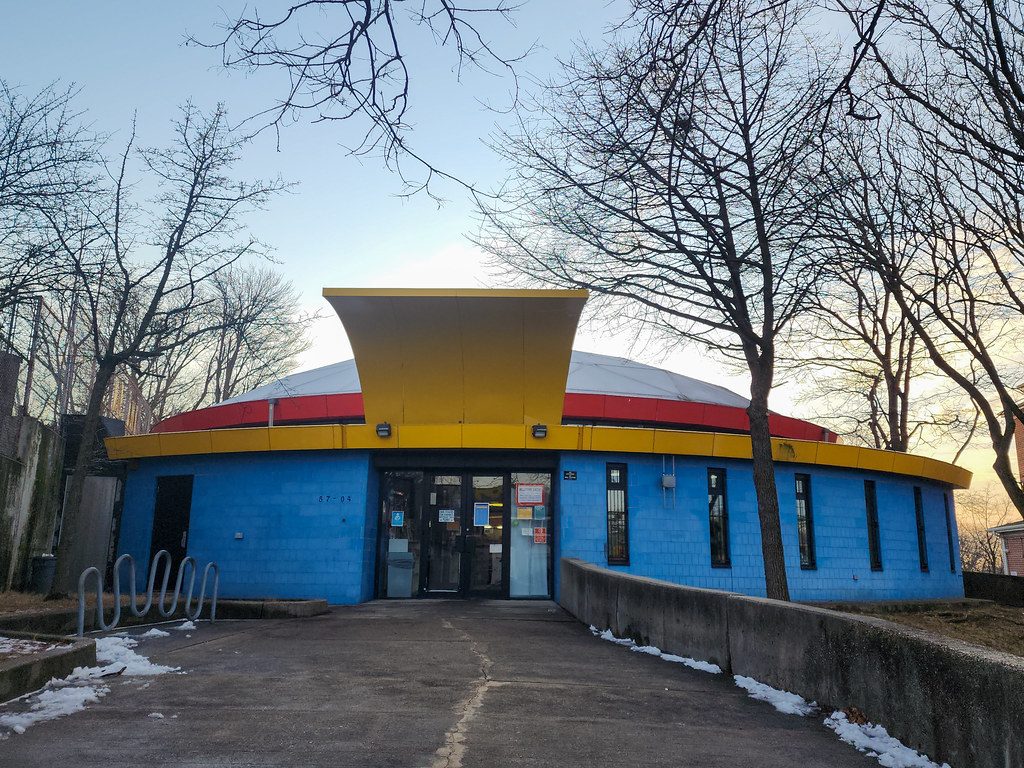
A ransomware attack hit the Queens Public Library on Wednesday, knocking out the website, public Wi-Fi, checkout and return machines, on-site computers, the mobile app and digital media services across all 66 branches. The branches themselves stayed open, and patrons could still check books out in person.

No group has claimed the attack, and officials say they do not yet know who is behind it or whether patron data was exposed. Chief executive Dennis Walcott said the library is working with the New York Police Department and the FBI. The last major library ransomware case, at the British Library in 2023, took years and millions of dollars to recover from.

Why it matters

Public libraries hold patron records and run on thin budgets, making them soft targets whose recovery can take months or years.

Last Monday's email for New York, NY

Sent Nov 2. It carried:

Get next Monday's: one short email a week. Free. Unsubscribe in one click.

Questions about this story

Free account needed to ask — your question is kept and asked for you right after sign-up. Answers are public.

No questions yet — be the first to ask.

Key Indicators

66
Branches in the Queens Public Library system
All locations remained open to the public during the outage.
6
Core services knocked offline
Website, on-site computers, checkout and return machines, Wi-Fi, app and digital media.
0
Ransomware groups publicly claiming the attack
No established gang had claimed responsibility as of Thursday.

Voices

Curated perspectives — historical figures and your fellow readers.

Sign up to generate historical perspectives on this story.

People Involved

Organizations Involved

Timeline

October 2021 November 2026

3 events Latest: Today
  1. Outage continues; FBI and NYPD join investigation

    Today Response

    Branches stay open for in-person checkout. Officials say they do not know who is behind the attack or if data was exposed.

  2. Ransomware attack hits Queens Public Library

    Cyberattack

    The attack downs the website, public Wi-Fi, checkout and return machines, on-site computers, the app and digital media services.

  3. Queens Public Library ends daily late fines

    Policy

    The library permanently eliminated daily late fines on circulating materials, a policy that kept patrons fine-free during the outage.

Scenarios

1

Library restores systems within weeks, no patron data confirmed exposed

Possible Resolves by End of 2026

Discussed by: Library officials and security analysts cited by The Register

The library's IT department rebuilds the network, the investigation finds no data was taken, and no ransom is paid. Branches return to normal service before the end of the year. This is the outcome most public institutions aim for, though the British Library case shows how rarely it arrives on schedule.

2

Ransomware gang claims attack and leaks patron data

Uncertain Resolves by Jan 31, 2027

Discussed by: Cybersecurity trade press, including The Register

A named ransomware group posts the Queens Public Library to its leak site, claims to have stolen patron or staff records, and threatens to publish them. That would turn a service outage into a privacy incident affecting library users, who may have had contact details and borrowing histories on file.

3

Outage drags on for months, mirroring the British Library

Possible Resolves by Q2 2027

Discussed by: Security analysts cited by The Register

Recovery stalls as the library rebuilds systems piece by piece, leaving some services degraded for months. The British Library's 2023 attack followed this path: its recovery was still incomplete in its 2025/26 annual report, with full restoration not expected until the end of 2026.

Historical Context

3 moments from history that rhyme with this story — and how they unfolded.

October 2023

British Library ransomware attack (2023)

The Rhysida ransomware gang breached the British Library, locking staff out of the catalog and taking the website offline. The library refused the gang's 20 Bitcoin ransom demand and chose to rebuild its systems instead.

Then

Staff worked without a functioning catalog for weeks, and the library drained reserves to fund an IT rebuild costing millions.

Now

Recovery was still incomplete in the library's 2025/26 annual report, with full restoration of electronic resources not expected until the end of 2026.

Why this matters now

It is the closest precedent for a major library ransomware attack and shows how long recovery can take even when the victim refuses to pay.

March 2018

Atlanta SamSam ransomware attack (2018)

The SamSam ransomware crippled city of Atlanta computer systems, taking down court, permit and payment systems. City staff reverted to paper forms and manual processing for weeks.

Then

Residents could not pay bills or file permits online, and the city spent millions on recovery and new security.

Now

The attack became a reference case for how under-resourced public agencies recover from ransomware, and it prompted cities to reassess backup and incident-response plans.

Why this matters now

It shows the pattern Queens now faces: a public agency with limited IT budgets forced into a slow, costly manual fallback.

May 2017

WannaCry attack on the UK National Health Service (2017)

The WannaCry worm encrypted computers across NHS trusts in England and Scotland, forcing staff to cancel appointments and divert patients. Thousands of appointments and operations were disrupted.

Then

Hospitals ran on paper and diverted emergency cases while systems were restored over several days.

Now

The attack exposed how far behind public institutions were on basic security patching and led to new national guidance and funding for NHS cyber resilience.

Why this matters now

It is the clearest example of ransomware hitting a public service that people depend on daily, and of the operational workarounds staff improvise when systems go dark.

Sources

(2)