Pull to refresh
Logo
Pre-auth bug in 32-year-old GNU telnetd enables remote code execution on unpatched systems

Pre-auth bug in 32-year-old GNU telnetd enables remote code execution on unpatched systems

New Capabilities

CVE-2026-32746 lives in the LINEMODE SLC handler, executes before login, and ships on most major Linux distributions

Yesterday: watchTowr publishes deep exploitation analysis

Overview

Updated 1 hour ago

In March 2026, researchers found a buffer overflow in GNU telnetd that had hidden in the codebase for roughly 32 years. The flaw, tracked as CVE-2026-32746, lets a remote attacker corrupt server memory before the login prompt ever appears. Because most Linux distributions and countless embedded devices base their telnet daemons on GNU inetutils, the vulnerable code ships almost everywhere.

The bug sits in the LINEMODE SLC handler, telnet's feature for negotiating character control. Around 40 specially crafted triplets overflow a fixed 108-byte buffer and corrupt a write pointer the server uses later, producing arbitrary writes and frees before login. The upstream fix is three lines; the hard part is the long tail of unpatched routers, industrial controllers, and appliances.

Why it matters

A pre-auth bug in a 32-year-old network daemon on routers, industrial controllers, and Linux servers lets remote attackers gain root without credentials.

Questions about this story

Free account needed to ask — your question is kept and asked for you right after sign-up. Answers are public.

No questions yet — be the first to ask.

Key Indicators

32 years
Years the bug went undetected
Introduced around 1994; researcher watchTowr notes Kurt Cobain was still alive when the hole first appeared.
9.8
CVSS 3.1 severity score (critical)
Rated critical because no authentication is required to trigger the overflow.
108 bytes
Size of the overflowed buffer
A fixed slcbuf that roughly 40 SLC triplets push past, corrupting the adjacent write cursor.
3 lines
Lines in the upstream patch
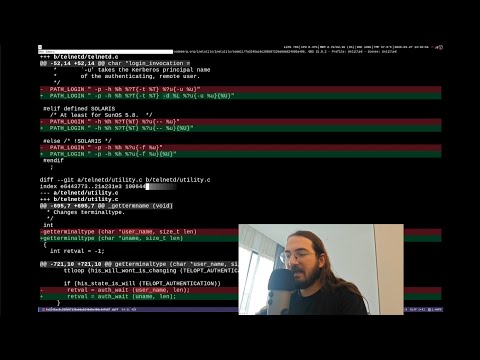
A single bounds check in add_slc() discards writes that would overrun the buffer.

Voices

Curated perspectives — historical figures and your fellow readers.

Ever wondered what historical figures would say about today's headlines?

Sign up to generate historical perspectives on this story.

People Involved

Organizations Involved

Timeline

January 1994 September 2026

8 events Latest: Yesterday
Tap a bar to jump to that date
  1. watchTowr publishes deep exploitation analysis

    Latest Research

    Labs assessment finds arbitrary free and pointer leak; x86-64 exploitation hard.

  2. Dream Security publishes public advisory

    Disclosure

    Firm details the pre-auth LINEMODE SLC overflow for the public.

  3. Major Linux distributions ship patches

    Patch

    Debian, Ubuntu, Red Hat, SUSE, and Arch push fixed inetutils packages.

  4. CVE-2026-32746 assigned, advisories begin

    Disclosure

    CVE number assigned; downstream distribution advisories roll out.

  5. Maintainer opens the fix and approves coordinated disclosure

    Fix

    Collin Funk opens PR #17, a three-line bounds check in add_slc().

  6. Dream Security reports the flaw to GNU Inetutils

    Discovery

    Research team files initial report on the pre-auth overflow.

  7. Client-side sibling patched as CVE-2005-0469

    Fix

    Same unchecked write fixed in GNU telnet client; server-side twin missed.

  8. Bug introduced into GNU inetutils telnetd

    Origin

    LINEMODE SLC handler gains an unchecked buffer write, circa early 1994.

Scenarios

1

Telnetd flaw sparks a worm or mass botnet campaign

Unlikely Resolves by Q2 2027

Discussed by: watchTowr and Dream Security researchers, who both flag the wide blast radius of inetutils-derived telnetd code

An attacker chains the pre-auth overflow into code execution on a common embedded target — MIPS routers or ARM industrial controllers, where watchTowr found constraints far looser than on x86-64. That weaponized code gets folded into botnets that sweep internet-facing telnet, echoing how EternalBlue powered WannaCry. So far no public exploit has been disclosed.

2

Patch wave closes the telnet exposure quietly

Likely Resolves by Mar 18, 2027

Discussed by: Debian, Ubuntu, and Red Hat maintainers, who patched within days; enterprise security teams that disabled telnetd

The upstream fix ships everywhere, and the telnet daemon — rarely internet-facing already — gets removed from the remaining systems still running it. No confirmed mass exploitation emerges, and the CVE joins the pile of patched-and-forgotten flaws. Security teams cite asset visibility and service retirement rather than exploit risk as the lasting lesson.

3

Long-tail embedded devices carry the exposure for years

Possible Resolves by Q2 2027

Discussed by: watchTowr's embedded-focused analysis; ICS-CERT and vendor security teams tracking industrial gear

No broad worm materializes, but targeted attackers pick off unpatched embedded telnetd on routers, storage appliances, and lab gear where patching is slow or impossible. Incident reports surface piecemeal through vendor advisories, never rising to a single mass event. The bug effectively becomes a permanent backdoor on devices that will never be updated.

Historical Context

3 moments from history that rhyme with this story — and how they unfolded.

March 2005

CVE-2005-0469 (2005)

The GNU telnet client had the same unchecked write in SLC reply handling: a malicious server could crash or compromise the client. It was patched in the client in 2005. The server-side equivalent in telnetd was overlooked and stayed live for 21 more years.

Then

Client fixed; telnetd's mirrored flaw went unnoticed.

Now

The 2026 disclosure exposed the same bug class, same code family, caught only on one side.

Why this matters now

Shows how a single parsing routine can hide a flaw for decades when only one endpoint gets audited. The 2026 fix finally closed the server-side twin.

April 2014

Heartbleed (2014)

OpenSSL shipped for two years with an unbounded memory read in its TLS heartbeat extension, letting any remote attacker pull 64KB of memory from HTTPS servers. The leak exposed private keys, passwords, and session data across half the web.

Then

A frantic global patching wave; cloud providers rotated keys and certificates en masse.

Now

Spurred the Core Infrastructure Initiative and renewed funding for auditing foundational open-source code.

Why this matters now

Like telnetd, Heartbleed was a flaw in software assumed trustworthy that shipped everywhere. It set the template: coordinated disclosure, rapid distro patching, and a long cleanup tail for systems nobody remembers running the service.

April–May 2017

EternalBlue and WannaCry (2017)

The NSA-developed EternalBlue exploit targeted MS17-010, a pre-auth remote code execution hole in Windows SMBv1 that shipped since 2003. The Shadow Brokers leaked it in April 2017, and WannaCry used it weeks later to encrypt over 200,000 machines in 150 countries within days. NotPetya followed with even more destructive intent.

Then

Hospitals, shippers, and manufacturers ground to a halt; Microsoft patched even unsupported Windows XP.

Now

Proved that pre-auth bugs in legacy protocols many admins assumed were internal-only can go wormable overnight.

Why this matters now

Telnet, like SMBv1, is a decades-old pre-auth protocol still present on reachable systems. The telnetd bug holds the same worm potential on any population of exposed devices.

Sources

(10)