Pull to refresh
Logo
Austin ISD staff social security numbers exposed in data breach

Austin ISD staff social security numbers exposed in data breach

Force in Play Austin, TX local

KVUE reports staff social security numbers were among the compromised data

Overview

Updated 14 hours ago

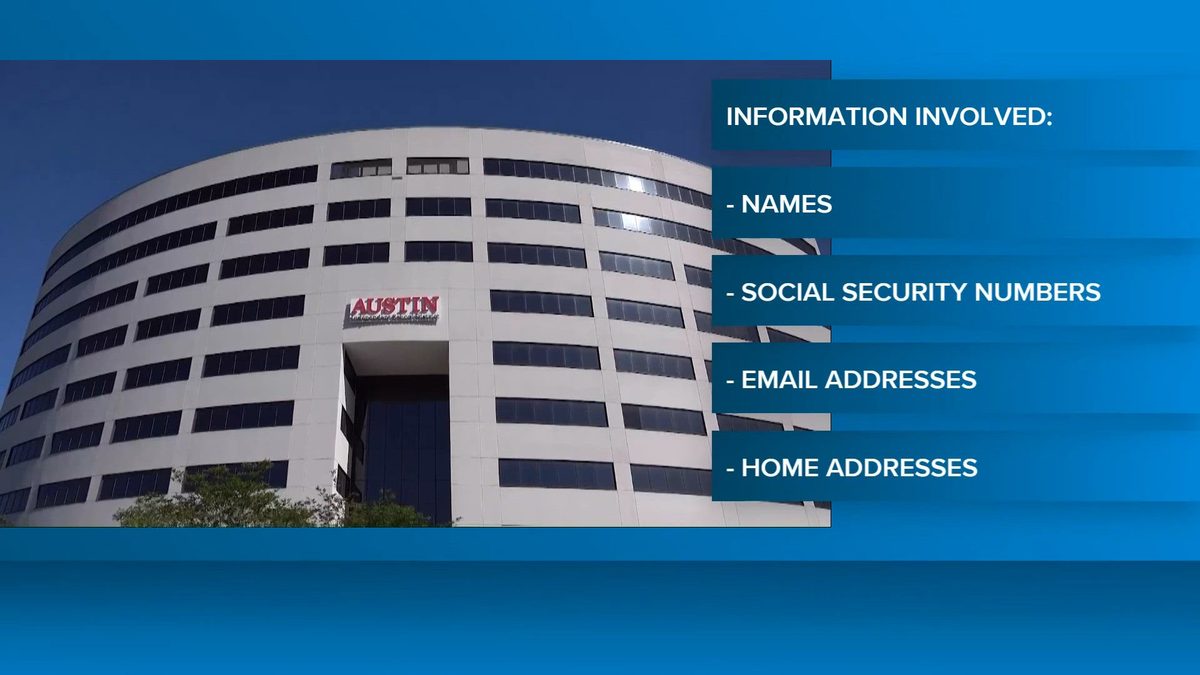
Austin Independent School District staff had their personal information, including social security numbers, compromised in a data breach, according to a KVUE report published October 26. The report did not name the software system breached or how many employees were affected.

Social security numbers are among the most sensitive forms of personal data. If the stolen records are sold or leaked, Austin ISD employees face years of identity theft and financial fraud risk.

Why it matters

Stolen staff social security numbers put Austin ISD employees at lasting risk of identity theft and financial fraud.

Monday: what changed in Austin, TX

One short email a week with the openings, closings, permits and council votes we covered. Free. Unsubscribe in one click.

Questions about this story

Free account needed to ask — your question is kept and asked for you right after sign-up. Answers are public.

No questions yet — be the first to ask.

Key Indicators

Included
Sensitive data compromised
Staff social security numbers were among the compromised data, per KVUE.
2026-10-26
Breach reported
KVUE published the report on October 26, 2026.

Voices

Curated perspectives — historical figures and your fellow readers.

Sign up to generate historical perspectives on this story.

Organizations Involved

Timeline

April 2026 October 2026

5 events Latest: Yesterday
Tap a bar to jump to that date
  1. Report: staff social security numbers exposed

    Latest Disclosure

    KVUE reported a data breach compromised Austin ISD staff personal information, including social security numbers.

  2. Austin ISD suspends BLEND after ShinyHunters claim

    Response

    The district removed platform access after a hacker posted a ransom message on BLEND; services were later restored.

  3. Instructure revises: student data involved

    Update

    The vendor told Austin ISD that student information was affected, after initially saying it was not.

  4. Instructure alerts Austin ISD

    Disclosure

    Instructure notified the district of unauthorized access, initially reporting no impact on student data.

  5. Attacker gains access to Instructure systems

    Incident

    A threat actor gained unauthorized access to Instructure's systems, beginning the incident later disclosed to schools.

Scenarios

1

Austin ISD confirms scope and offers credit monitoring

Likely Resolves by Feb 28, 2027

Discussed by: Austin ISD's own communication pattern after the May 2026 incident

The district completes its investigation, notifies affected staff, and offers identity protection services such as credit monitoring. This is the standard response when social security numbers are exposed, and the district has already shown it will issue public updates after security incidents.

2

Additional data types or systems found exposed

Possible Resolves by Q1 2027

Discussed by: The pattern of the May Instructure incident, which expanded from 'no impact' to student data involvement

Investigation reveals the breach went beyond staff social security numbers, touching student records, more staff data, or additional systems. The May 2026 Instructure breach followed this arc, starting with narrower claims and then widening.

3

Texas state inquiry opens into the breach

Uncertain Resolves by Q2 2027

Discussed by: Texas data breach notification requirements to the state Attorney General

Texas authorities open an inquiry into whether Austin ISD met its data protection and notification duties. The state Attorney General's office has shown willingness to investigate school district matters, though the record does not confirm it has acted here.

Historical Context

2 moments from history that rhyme with this story — and how they unfolded.

December 2024 – January 2025

PowerSchool data breach (2024-2025)

PowerSchool, a student information system vendor used by thousands of school districts, disclosed that attackers using stolen credentials accessed records of students and staff. In some cases, social security numbers were among the exposed data.

Then

Districts notified families and offered credit monitoring; PowerSchool reportedly paid the threat actor to delete the stolen data.

Now

The breach became a cautionary example of how one education vendor's security lapse can expose records across many districts at once.

Why this matters now

Like the Instructure incident, PowerSchool shows that a single vendor breach can put staff and student data across many districts at risk, the same dynamic now facing Austin ISD.

2015

OPM data breach (2015)

Hackers breached the US Office of Personnel Management, stealing background-investigation records of roughly 22 million current and former federal employees and contractors, including social security numbers.

Then

The government offered affected individuals credit monitoring and launched a review of federal cybersecurity practices.

Now

The breach remains a reference point for the long-lasting identity theft risk that follows social security number exposure.

Why this matters now

OPM demonstrates that once social security numbers are stolen, the fraud risk persists for years, which is the concern Austin ISD staff now face.

Sources

(3)