Pull to refresh
Logo
Denmark data breach exposes personal data of millions of citizens

Denmark data breach exposes personal data of millions of citizens

Force in Play

Attackers stole names, addresses, and CPR numbers of 8.8 million people from the national registry

2 days ago: Ministry announces breach affecting 8.8 million people

Overview

Updated 1 hour ago

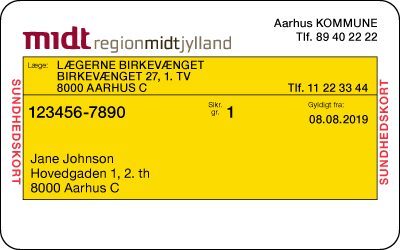
Hackers broke into Denmark's national population register and pulled personal data on 8.8 million people - names, addresses, and social security numbers. The haul covers about 80% of the register's 11 million records, including people who have died or moved abroad.

The attackers got in by abusing a private Danish company's legitimate access to the registry, and the access lasted about 10 days in September. Danish authorities call it likely the largest data breach in the country's history, and they warn the stolen data could fuel targeted fraud.

Why it matters

If the stolen data feeds fraud campaigns, millions of Danes face targeted phishing and identity scams using their real names, addresses, and CPR numbers.

Questions about this story

Free account needed to ask — your question is kept and asked for you right after sign-up. Answers are public.

No questions yet — be the first to ask.

Key Indicators

8.8 million
People whose data was compromised
Names, addresses, and CPR numbers of registered people, including the deceased and those who emigrated.
11 million
Total records in the CPR register
The breach covered about 4 in 5 records in the national population register.
80%
Share of register records exposed
The ministry's figure is preliminary and not yet final.
10 days
Duration of unauthorized access
Access ran through September 2026 via a small Danish company's lawful account.

Voices

Curated perspectives — historical figures and your fellow readers.

Ever wondered what historical figures would say about today's headlines?

Sign up to generate historical perspectives on this story.

People Involved

Organizations Involved

Timeline

September 2026 October 2026

4 events Latest: 2 days ago
Tap a bar to jump to that date
  1. Ministry announces breach affecting 8.8 million people

    Latest Announcement

    Minister Christina Egelund announced the breach, called it deeply serious, and requested a full security review.

  2. CPR administration notifies Datatilsynet

    Notification

    Over the weekend the administration learned the extent of the access and notified the data protection agency.

  3. CPR administration notices unusual activity

    Discovery

    An employee noticed irregular activity on Friday evening; the company's access was cut off.

  4. Unauthorized access to CPR system begins

    Incident

    Attackers abused a small Danish company's lawful access to search the CPR register, lasting about 10 days.

Scenarios

1

Police identify and charge those behind the CPR breach

Possible Resolves by Apr 5, 2027

Discussed by: Danish police and Datatilsynet, which are investigating with access to the CPR security log

The security log records which companies made searches, and the breach was precisely pinpointed to a 10-day window in September. Police have prior experience with similar cases, including a 2025 case where an intern sold registry details to a gang. An arrest or formal charges would confirm the attackers' identity and motive.

2

Stolen CPR data fuels a documented fraud campaign

Possible Resolves by Apr 5, 2027

Discussed by: Danish authorities, who warn the data could be used for targeted phishing

The ministry warns that stolen names, addresses, and CPR numbers could be used in fraud attempts. Scammers could use the real data to make fake calls, texts, or emails sound genuine - for example, a fake bank call claiming an account is at risk. A documented campaign would show the data's real-world impact.

3

Security review leads to CPR system reforms

Likely Resolves by Apr 5, 2027

Discussed by: Minister Christina Egelund, who requested a full security review

Egelund has asked for a thorough security review of the CPR system and said measures are already underway to prevent a repeat. The review could lead to new security requirements for companies with registry access, or legislative changes to the CPR Act. The ministry has not detailed the measures already begun.

Historical Context

2 moments from history that rhyme with this story — and how they unfolded.

2016

Turkey national ID breach (2016)

A breach exposed records of millions of Turkish citizens, including national ID numbers, addresses, and other personal data. The data was reportedly offered for sale online.

Then

The Turkish government downplayed the breach while the data circulated online.

Now

It became a reference point for the scale of damage a national identity database breach can cause.

Why this matters now

Like Denmark's CPR, Turkey's national ID database held permanent, hard-to-revoke identity data that became a high-value target for fraud.

2017-present

India Aadhaar database exposures (2017-present)

India's Aadhaar national ID database, holding biometric and personal data on over a billion people, has faced repeated data exposure incidents since 2017, including leaked access portals and data sold on messaging apps.

Then

Each exposure triggered investigations and promises of tighter security.

Now

The repeated incidents showed that national identity systems become permanent targets because the data cannot be changed or revoked.

Why this matters now

Aadhaar's repeated exposures illustrate why a breach of Denmark's CPR register is so serious - the stolen identity data remains valid and usable for years.

Sources

(11)