
May 2023
Barracuda ESG zero-day (2023)
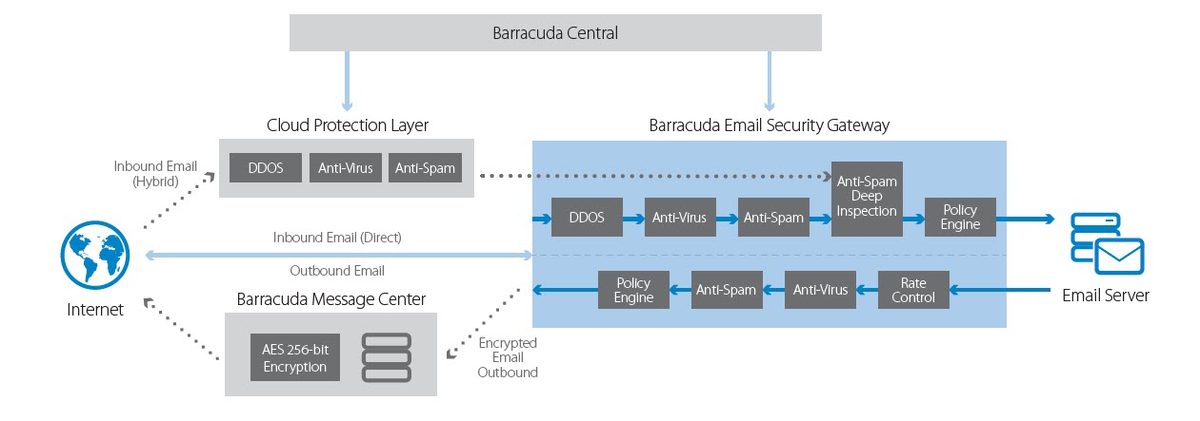
Barracuda disclosed CVE-2023-2868, a command injection in its Email Security Gateway that had been exploited since October 2022 by a group tracked as UNC4841. The company told customers to replace affected appliances rather than simply patch them.
Then
Barracuda shipped replacement hardware and took affected devices out of service.
Now
The incident established that edge email gateways are high-value targets and that patching alone may not be enough after a compromise.
Why this matters now
The same product line is at the center of this chain, and the 2023 response shows how Barracuda has handled root-level bugs in the past.