Pull to refresh
Logo
Massive leak exposes records of 41,000 DHS workers, including undercover agents

Massive leak exposes records of 41,000 DHS workers, including undercover agents

Force in Play

Hacktivists publish searchable database of DHS staff, contractors, and the surveillance tools they use

Overview

Updated Yesterday

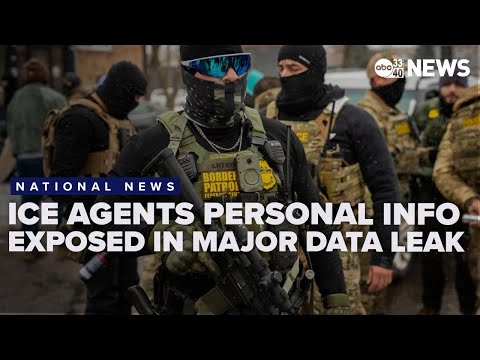
On October 28, the transparency nonprofit Distributed Denial of Secrets (DDoSecrets) published a searchable archive of more than 41,000 Department of Homeland Security (DHS) employees and contractors. The data, named "Icepick," includes names, phone numbers, office addresses, job titles, and each person's supervisor, covering DHS and seven of its agencies, including Immigration and Customs Enforcement (ICE), Customs and Border Protection (CBP), and the Cybersecurity and Infrastructure Security Agency (CISA).

The records were pulled from DHS's Okta login system, which Okta says was not breached. The files double as an operations manual: internal permission-group names reference surveillance tools, wiretap programs, and certified undercover operations, and roughly 10,000 ICE personnel appear in the archive. The records were last updated on August 19, 2026.

Why it matters

The leak is a searchable roster of DHS agents, contractors, and surveillance programs—and a targeting list for anyone who wants to find them.

Questions about this story

Free account needed to ask — your question is kept and asked for you right after sign-up. Answers are public.

No questions yet — be the first to ask.

Key Indicators

41,000+
DHS employees and contractors exposed
Roughly a seventh of DHS's workforce, spanning DHS and seven component agencies.
21,000
Customs and Border Protection personnel
CBP staffers account for more than half of the records in the archive.
10,000
ICE personnel in the leak
About a third of them belong to Homeland Security Investigations, ICE's investigative wing.
7
DHS component agencies affected
Includes ICE, CBP, USCIS, CISA, and three other agencies.
1,300
ICE enforcement accounts created since July 2025
Accounts created after the One Big Beautiful Bill Act funded 10,000 new ICE officers.

Voices

Curated perspectives — historical figures and your fellow readers.

Sign up to generate historical perspectives on this story.

People Involved

Organizations Involved

Timeline

2014 October 2026

7 events Latest: Yesterday
Tap a bar to jump to that date
  1. DDoSecrets publishes 'Icepick' archive

    Latest Data breach

    Searchable database of 41,000+ DHS staff and contractors goes public, including undercover and surveillance program references.

  2. Leaked DHS records last updated

    Data

    The records in the Icepick archive were last updated on this date.

  3. Mullin promises to 'turn up the heat'

    Statement

    DHS Secretary Markwayne Mullin pledges stepped-up ICE operations; the Department of Peace cites this as its motivation.

  4. DHS notifies 250,000 of a breach

    Data breach

    DHS notified nearly 250,000 people of a breach at the department.

  5. DHS breach exposes 390,000 records

    Data breach

    A breach may have exposed data of 390,000 then-current and former DHS employees, applicants, and contractors.

Scenarios

1

Federal prosecutors charge the hackers behind Icepick

Possible Resolves by Q2 2027

Discussed by: WIRED; the administration has prosecuted critics under anti-doxing and stalking laws, and arrested suspects in the separate ShinyHunters FBI breach

The Justice Department opens a criminal investigation into the Department of Peace, DDoSecrets, or crimew. The administration's expansive reading of 18 USC 119 and its prior arrests make charges a live possibility, but the publisher's nonprofit status and the leak's public-interest framing cut against prosecution.

2

Okta or DHS confirms unauthorized access

Unlikely Resolves by Jan 31, 2027

Discussed by: Okta denies any breach; WIRED and CyberScoop report the data as coming from DHS's Okta login system

If forensic analysis confirms the DDoSecrets claim, Okta and DHS would face questions about how an attacker reached the identity system. The denial could also hold: the data may have been extracted via phishing, an admin account compromise, or an insider rather than a breach of Okta itself. Confirmation would trigger credential resets and a security audit across DHS.

3

Doxing prosecutions expand using the leak as justification

Possible Resolves by End of 2027

Discussed by: Adam Steinbaugh of FIRE; the administration's expanded definition of doxing covers publishing basic facts about employees

The administration could use the Icepick leak to argue that postings of agent names and titles constitute a threat, extending prosecutions under 18 USC 119 and related statutes. FIRE's Steinbaugh says most of the leaked data is the kind of info on a business card and cannot be criminalized. New charges would test that boundary in court.

4

Leaked data used to target DHS personnel

Possible Resolves by End of 2027

Discussed by: Alexander Leslie of Recorded Future, who calls the data an intelligence resource

A foreign intelligence service or activist group correlates the leaked records with other breached data to build target profiles of DHS staff, attempt impersonation, or map undercover operations. Recorded Future's Leslie says an adversary could spend months exploiting the relationships in the archive.

Historical Context

3 moments from history that rhyme with this story — and how they unfolded.

June 2020

BlueLeaks (June 2020)

Days after George Floyd protests swept the US, DDoSecrets published BlueLeaks, a 270-gigabyte trove of police department files from the records vendor Netsential. It included emails, intelligence bulletins, and internal training material from more than 200 agencies.

Then

The FBI investigated; no public criminal charges were filed against DDoSecrets. Several agencies reviewed what the leak revealed.

Now

BlueLeaks became a reference point for transparency publishers and a warning for law enforcement about vendor risk.

Why this matters now

The same publisher, DDoSecrets, released Icepick under the same rationale: expose the internal records of a government apparatus it sees as unaccountable.

July 2014

2014 DHS data breach

A contractor's mishandled data exposed the names, home addresses, and employment details of 390,000 DHS employees, job applicants, and contractors. The breach was blamed on a subcontractor's failure to secure data.

Then

DHS notified affected individuals and reissued credentials; the contractor faced scrutiny.

Now

The incident demonstrated how single points of failure in DHS's personnel data could expose large numbers of staff, a pattern the Icepick leak repeats at larger scale.

Why this matters now

DHS has a documented history of personnel-data exposure; Icepick adds identity-system access data on top of the earlier contact details.

2026

ShinyHunters FBI leak claim (2026)

A hacker group called ShinyHunters claimed to have stolen personal information on nearly every FBI employee and their families. Law enforcement agencies arrested several suspects and detained another alleged member.

Then

Arrests followed within weeks, signaling that the administration treats personnel-data theft as a priority crime.

Now

The arrests set a precedent for how federal investigators pursue groups that leak agent and employee records.

Why this matters now

It is the immediate precedent for how the government may respond to the larger Icepick leak of DHS personnel data.

Sources

(9)