Hadoop era permissions chaos (2010s)
Enterprises adopting Hadoop, Hive, and Spark in the mid-2010s faced a similar problem: data lake permissions lived in Ranger and Sentry policy stores that did not translate to downstream tools. Teams recreated access rules in every BI tool, and misconfigurations accumulated until breaches forced audits.
Cloudera and Hortonworks built Ranger and Sentry as central policy stores, but integration across vendors stayed fragmented.
The lesson stuck: centralized policy stores do not help unless every access path enforces them. That lesson directly shaped OneLake's security model and the authorized engine pattern.
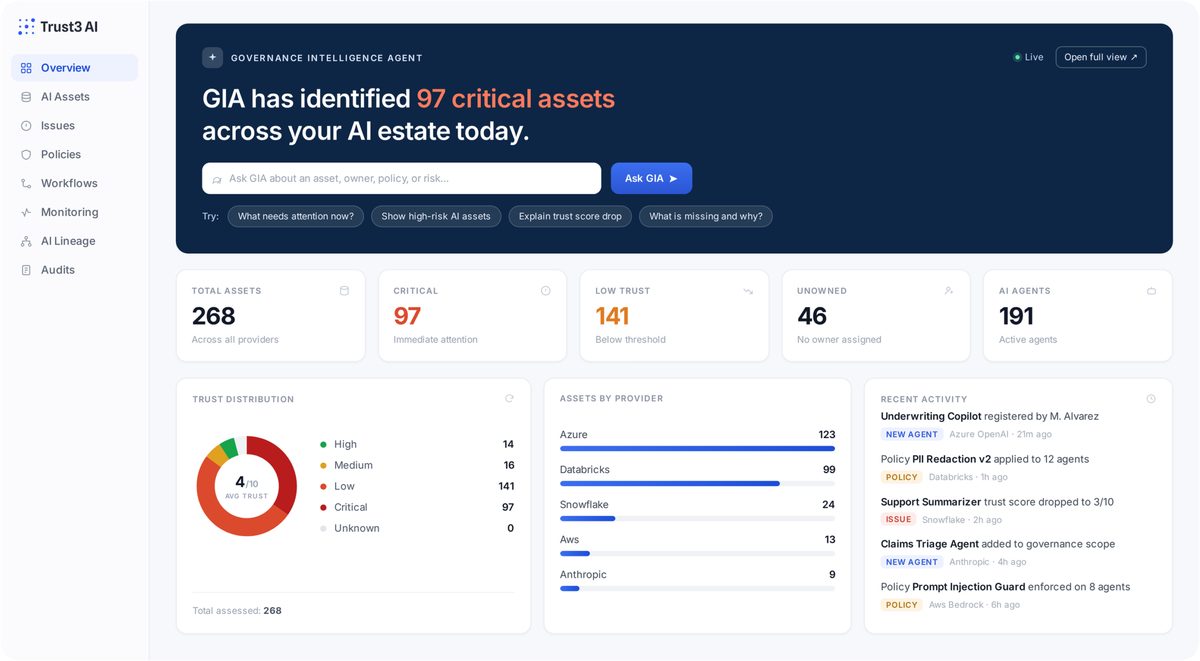
Trust3 AI's synchronization is an attempt to solve the same governance fragmentation problem for the modern stack, now complicated by autonomous agents that cannot be trusted to follow interactive-user conventions.